DFIR
Digital Forensics & Incident Response
When it happens — contain it, understand it, and prove it to a court.
What we do
Contain, understand,
then prove it.
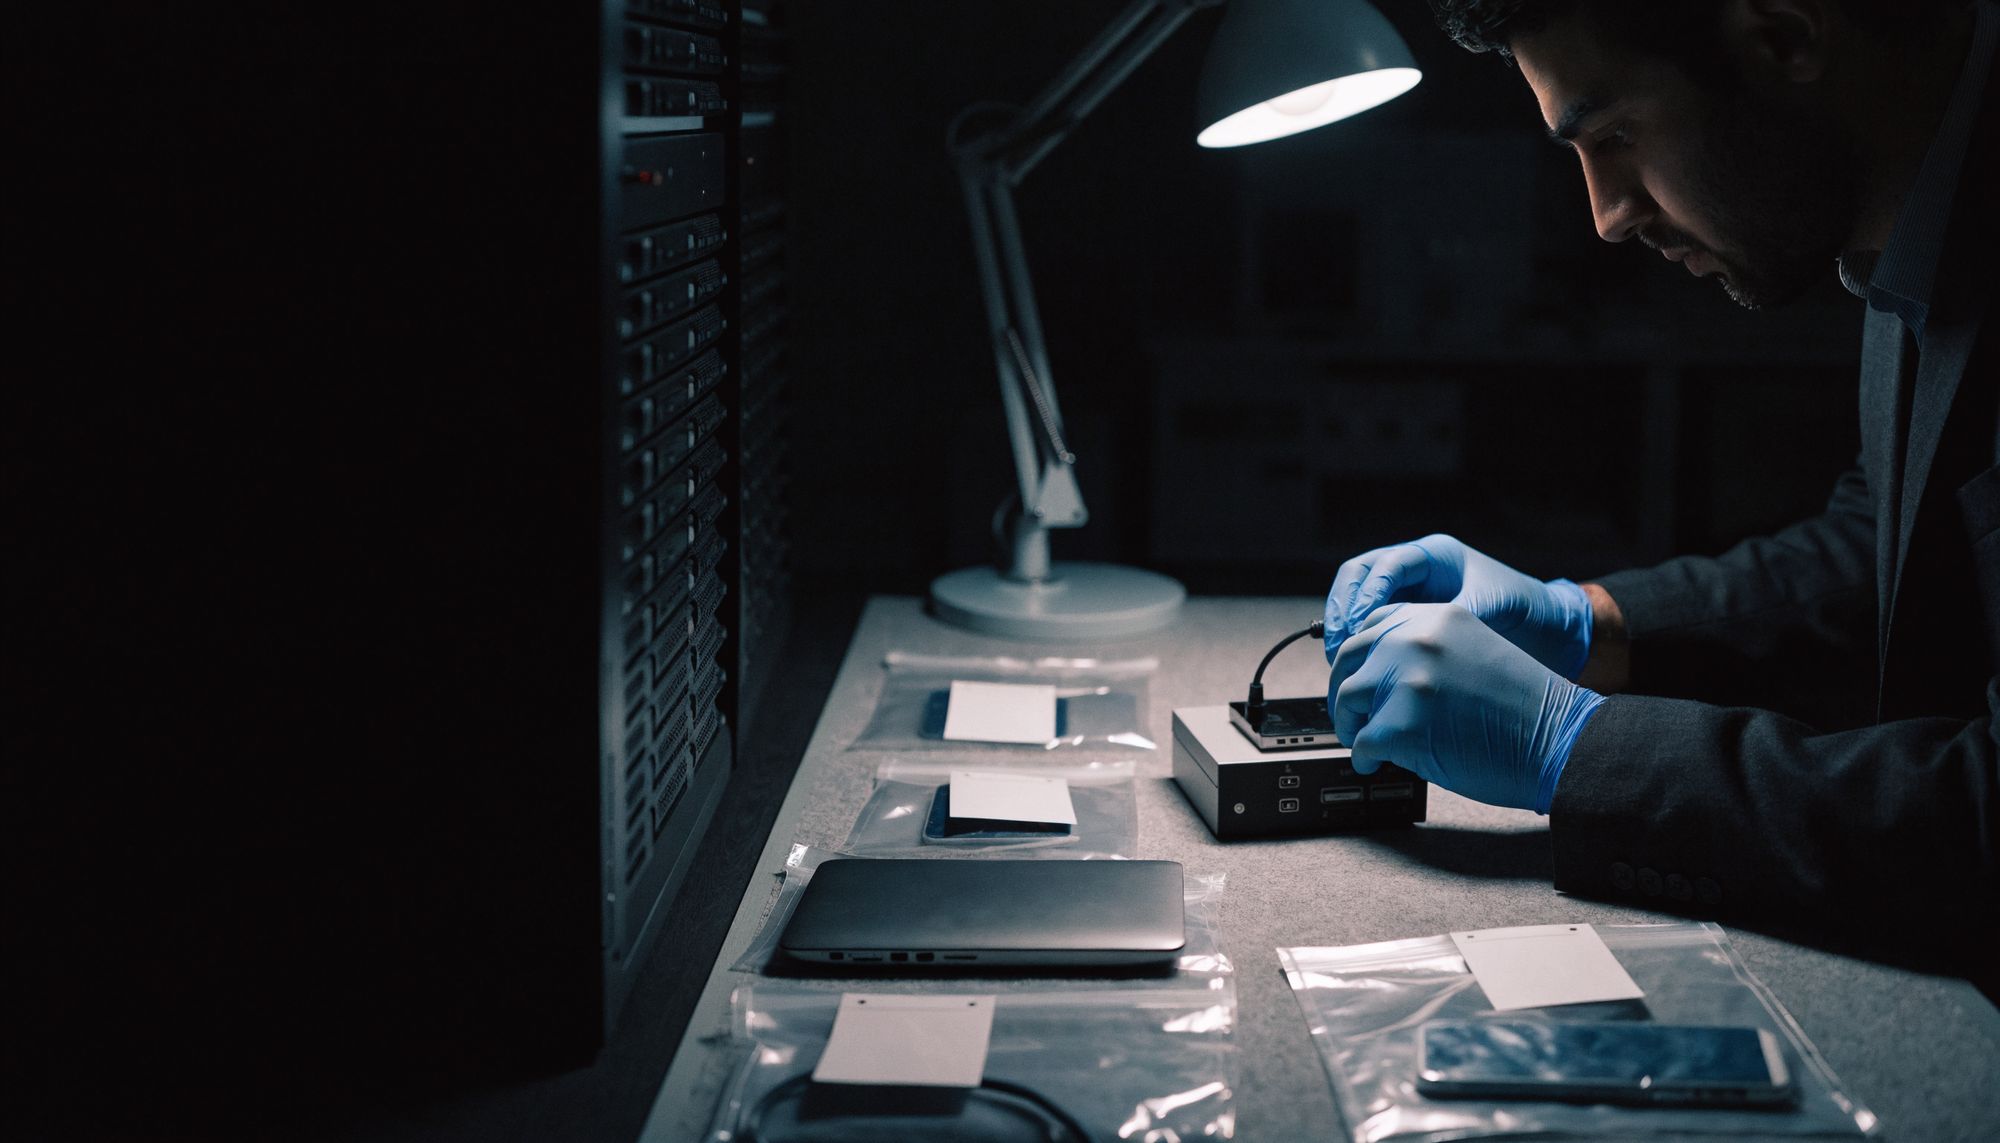
Investigations run to an evidential standard from the first acquisition, so findings hold up in legal and regulatory proceedings, not only in the post-incident report.
- Forensic acquisitionDisk, memory, mobile and cloud.
- Compromise assessments & eDiscoveryEstablish whether an adversary is present, and surface the records a legal matter needs.
- Malware analysisSandbox detonation and reverse engineering on a dedicated bench.
- Litigation-grade reporting & testimonyFindings written, and defended, for courts and regulators.
How we deliver
The response kit is
packed before the call.
Enterprise forensics, scalable endpoint DFIR and a malware bench, with retainer playbooks and breach-communication templates agreed in advance.
Incident Response Kit
 Timeline · root cause
Technology partners
Outcomes
Every incident leaves
the defences stronger.
Guaranteed-SLA IR retainers
Response commitments agreed in contract, not negotiated mid-incident.
SLA terms · to be confirmedChain of custody, preserved
Evidence handled for legal and regulatory proceedings from the first acquisition.
Root cause to SOC detection
Root cause becomes hardening recommendations, then new detections in the SOC.
How an incident runs
From the first call
to a closed case.
Contain
Scope the incident and limit the spread, with evidence captured before it is lost.
Understand
Acquire disk, memory, mobile and cloud evidence; analyse malware on the reverse-engineering bench.
Prove
Preserve chain of custody and deliver litigation-grade reporting, with testimony where needed.
Harden
Turn root cause into hardening recommendations and new SOC detections.
Related
Connected domains
Engage
Agree the response before the incident.
An IR retainer puts response playbooks and breach-communication templates in place before they are needed. Under attack right now? Report an incident instead.
partnerships@damanbayanat.com