Analysts with headsets in a darkened security operations center, facing a wide curved wall of network graphs and a world map

Delivery Platform

Core SOC & managed-services stack

The operational backbone that turns projects into 24×7 managed partnerships.

SOC · MDR · 24×7

The backbone

Everything behind the SLA.

The SOC platform, detection and intelligence, the managed-services stack and the incident-response kit — plus the offensive toolkit, cloud stack and academy behind every engagement.

SOC · MDR 24×7

Tiered L1–L3 analysts, a multi-tenant MSSP portal and detection-as-code behind every managed engagement.

01 – 04 · The core stack

Detect, decide,
respond, report.

Four layers every managed engagement runs on — from the first alert to the executive report.

Layer 01 · Core

Core SOC Platform

Where telemetry lands, is correlated and becomes a case.

  • SIEM / analyticsCortex XSIAM or Microsoft Sentinel
  • AutomationCortex XSOAR / Tines playbooks
  • EDR / XDRCrowdStrike & Cortex XDR telemetry
  • CasesCase management & multi-tenant MSSP portal
Palo Alto Networks Microsoft CrowdStrike

Layer 02 · Detect

Detection & Intelligence

Intelligence in, validated detections out.

  • Threat intelRecorded Future + Mandiant feeds
  • HuntingThreat hunting & detection-as-code (Sigma)
  • Digital riskDark-web & brand monitoring
  • Use casesPurple-team validated use-case library
Recorded Future
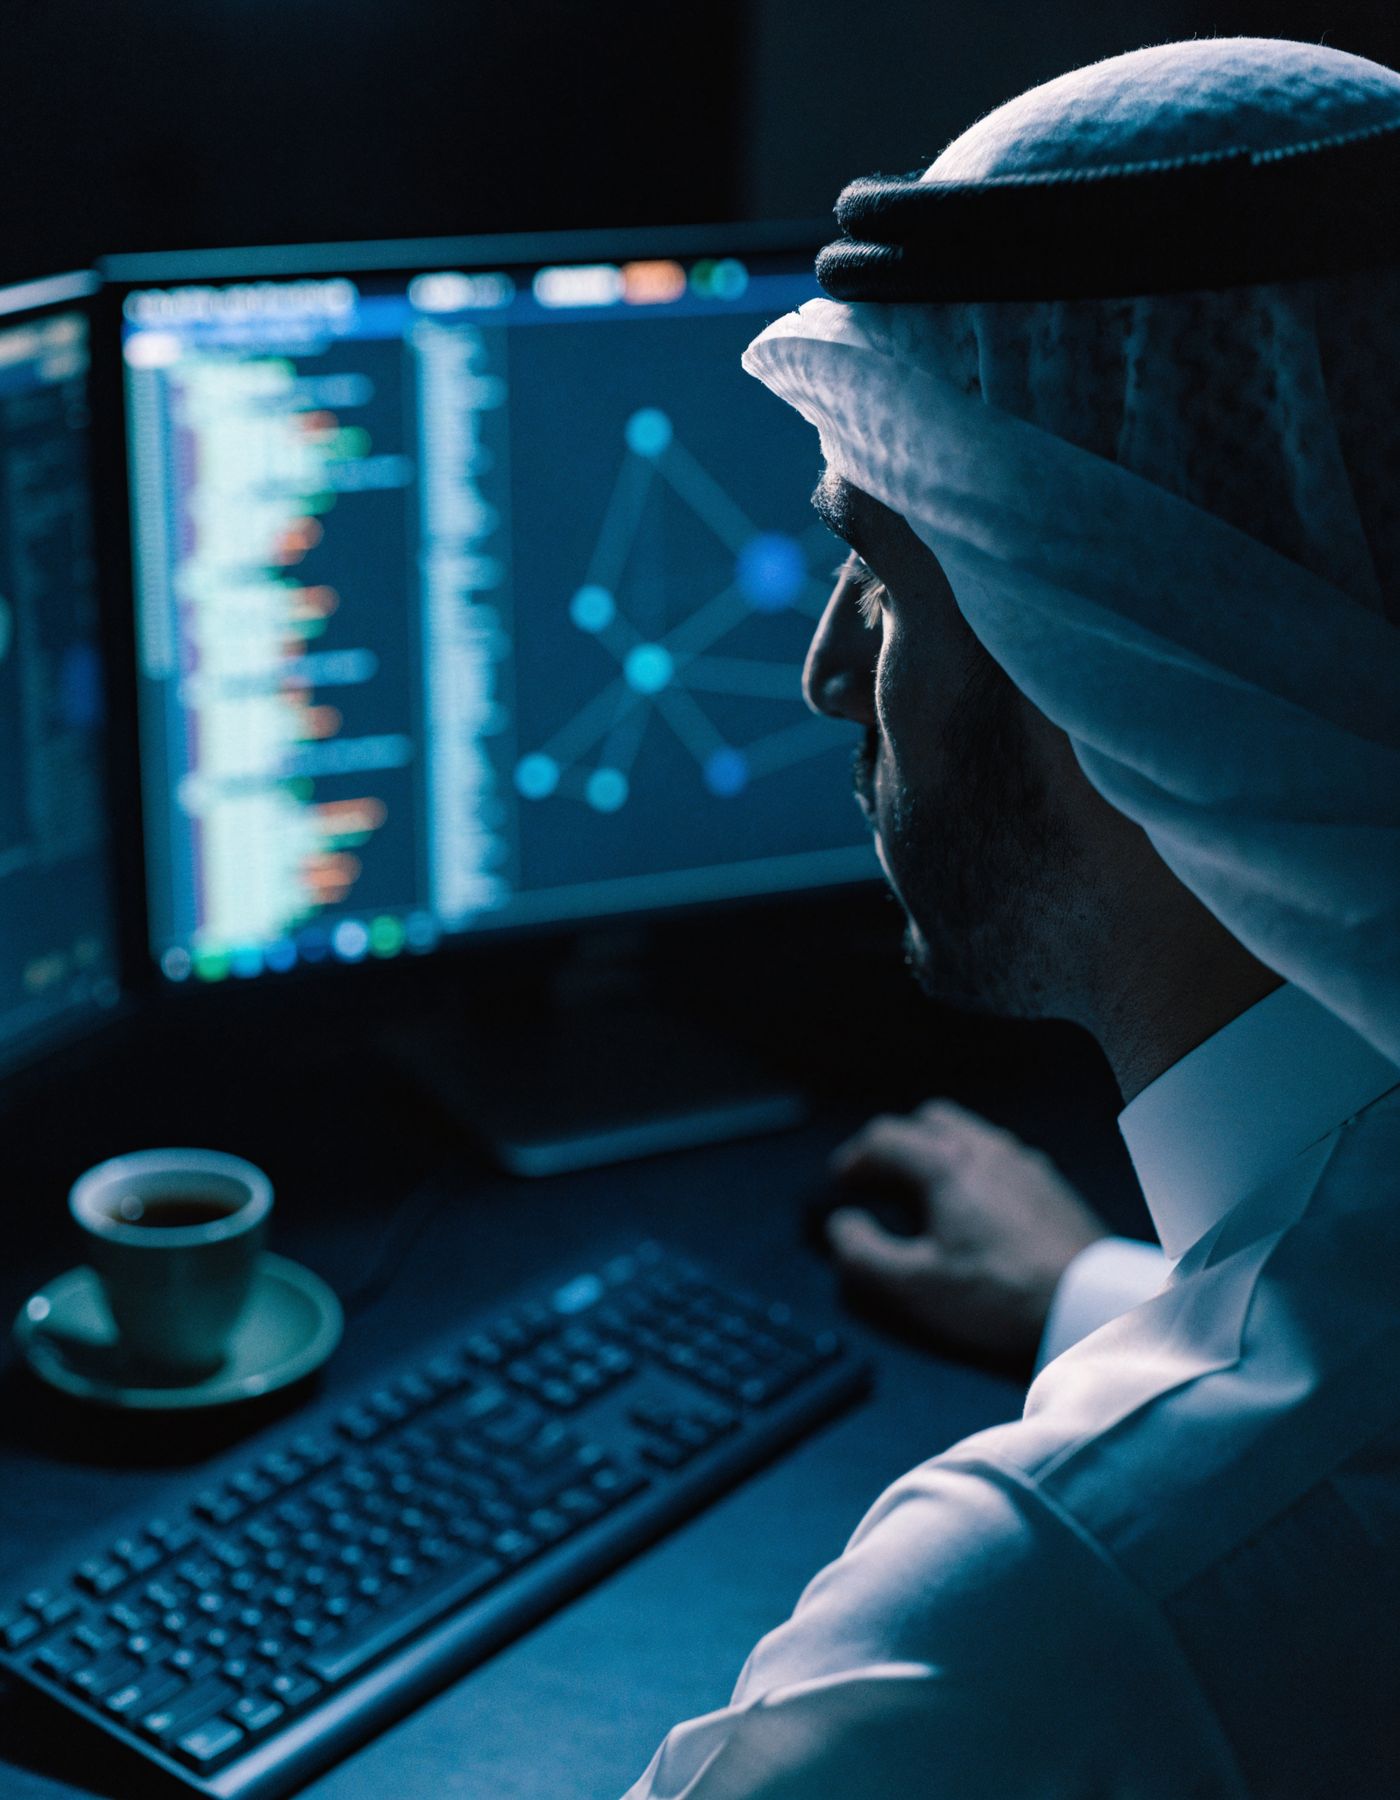
Threat hunter in a white thobe and ghutra working at two monitors of code and node graphs in a dark room
Detection · as code

Layer 03 · Manage

Managed Services Stack

The service layer every managed engagement runs on.

  • AssetsRMM & asset inventory across tenants
  • ITSMTicketing via ServiceNow / Jira
  • ReportingSLA dashboards & executive reporting
  • VulnerabilitiesVulnerability management (Tenable) as a service
Tenable

Layer 04 · Respond

Incident Response Kit

Ready before the call comes in.

  • ForensicsMagnet AXIOM · Binalyze AIR
  • Endpoint DFIRVelociraptor, at scale
  • AnalysisMalware sandbox & reverse-engineering bench
  • RetainerPlaybooks & breach-comms templates
Magnet Forensics Binalyze
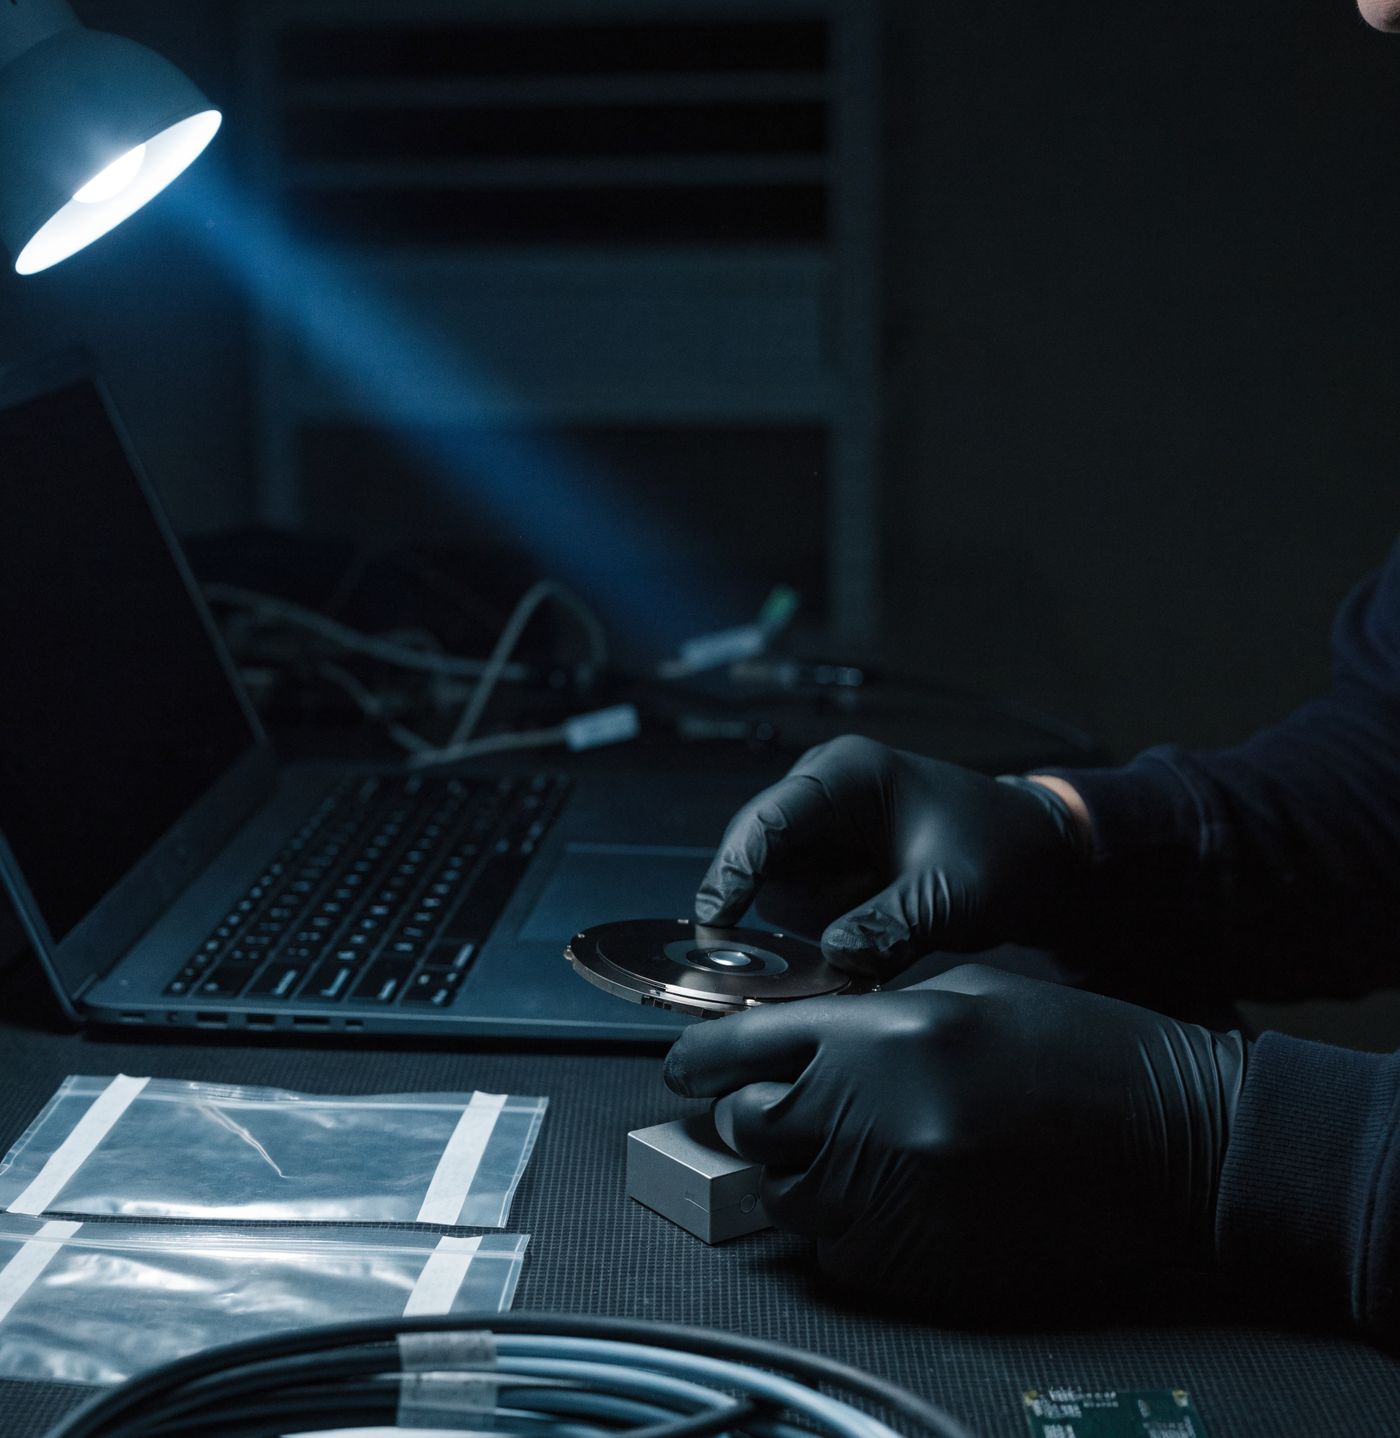
Gloved hands handling a hard drive on a forensics bench beside a laptop and sealed evidence bags
Chain of custody

05 – 07 · Offensive toolkit, cloud stack & academy

Toolkit, cloud
and academy.

The tooling, platforms and training environments behind every engagement.

Server corridor lit red on one side and blue on the other
Red-team bench
Layer 05 · Red-team bench

Penetration-Testing Toolkit

  • Kali / Parrot · Burp Suite Pro · Nessus / Nuclei
  • Cobalt Strike / Sliver C2 for red teaming
  • BloodHound · Impacket for AD attack paths
Offensive Security ↗
Rows of server racks in a dark data hall
Cloud & container
Layer 06 · Cloud & container

Cloud Security Stack

  • CNAPP: Wiz or Cortex Cloud (CSPM + CWPP)
  • IaC & container scanning in CI/CD
  • CSP-native guardrails (Azure / AWS / GCP)
  • Cloud IR & Kubernetes runtime protection
Cloud Security ↗
Analysts at workstations in a darkened training room while an instructor stands by a network-topology display
People & readiness
Layer 07 · People & readiness

Enablement & Academy

  • Awareness & phishing-simulation platform
  • Cyber range for analyst & client training
  • Vendor certification bootcamps
  • Executive & board tabletop exercises
Security Awareness ↗

How an engagement runs

Four steps,
one platform.

Every engagement follows the Daman Cybersecurity Delivery Model — and runs on the stack above.

Understand

Assess

Scoped discovery, gap analysis and exposure mapping.

Design & Implement

Engineer

Architecture, deployment and use-case engineering.

Monitor & Respond

Operate

24×7 SOC, SLA dashboards and executive reporting.

Improve & Adapt

Evolve

Purple-team validation, quarterly reviews and the roadmap.

Engage

See the stack behind the SLA.

Tell us what you need monitored. A senior consultant — not a sales desk — responds within one business day.

partnerships@damanbayanat.com